Loading

Vishing: What UK Law Firms Can Learn From the Canadian Attacks

TL;DR: Vishing (voice phishing) attacks broke into four of Canada’s biggest law firms in October. Criminals posed as IT staff on calls and Teams to steal account access and client files. The strongest defences are phishing-resistant sign-in and a simple rule that staff verify any unexpected IT request before acting on it.

What is vishing?

Vishing is phishing carried out by voice (voice phishing). The caller poses as someone your staff already trust, such as your own IT support. They then talk the person into handing over access.

It works because a phone call never passes through your email filters. The only thing standing between the caller and your systems is the person who picks up.

Microsoft Teams has made this easier for attackers. A call that appears to come from the helpdesk feels routine. That’s especially true in a busy firm where fee earners rarely meet the IT team in person.

How did vishing attacks break into Canadian law firms?

In late October, a coordinated campaign hit some of Canada’s best-known firms. McCarthy Tétrault, Davies Ward Phillips & Vineberg, Bennett Jones and Borden Ladner Gervais all confirmed breaches.

The attackers phoned staff or messaged them on Teams while posing as the firm’s own IT department. They raised password problems and security updates, then directed people to a fake Microsoft sign-in page.

At least seven employee accounts were compromised across the four firms. A source involved in the response told The Globe and Mail that around 31,000 files were taken from McCarthy Tétrault alone. Bennett Jones said the stolen data included client revenue reports. For some clients, it also included descriptions of the work the firm was doing for them.

The campaign used no software flaw. It relied on staff trusting a caller they believed was a colleague.

For a UK firm, the same breach would mean reporting to the ICO within 72 hours of becoming aware of it. It would also mean difficult conversations with every client whose files were taken.

Why didn’t multi-factor authentication stop the attackers?

The fake sign-in pages were built to get around multi-factor authentication (MFA). The page sat between the employee and the real Microsoft login, passing their details through as they typed.

The employee then approved the MFA prompt as normal. That gave the attacker the session that keeps a user signed in, so they had access without needing the password again.

Text message codes and app approvals can both be relayed this way. Passkeys and FIDO2 security keys are tied to the genuine website, so a fake page has nothing it can use. Our authentication solutions cover moving your firm onto stronger sign-in methods.

How can your law firm protect itself from vishing?
Start with a verification rule everyone knows. Nobody acts on an unexpected IT call or Teams message until they have called IT back on a number they already hold. Make it clear that genuine IT support should never need a password or an MFA code.

Next, look at who can contact your staff on Teams. If people outside your firm can message or call your team, limit it to the organisations you work with. Our Microsoft 365 support team can review these settings with you.

Your training needs to cover phone calls as well as emails. Most phishing exercises focus on the inbox, so a confident voice on a Teams call can catch people off guard. Fee earners juggling several matters are especially likely to go along with anything that makes a technical problem disappear. Our security awareness training helps staff recognise these approaches before they hand anything over.

Finally, keep watch on sign-ins. A login from a new device or location shortly after a helpdesk call is a strong warning sign. When an account looks compromised, revoke its active sessions, because a password reset alone may leave the attacker signed in. Managed security services give you that monitoring on an ongoing basis.

How can Labyrinth Technology help?

Labyrinth Technology has supported law firms across the UK for over a decade. We can review how your staff sign in to Microsoft 365. We can also help your team spot a fake IT call before it costs you client files.

If you would like to talk through where your firm stands, get in touch.

What Is an AI Worm and Should Your Law Firm Be Concerned?

TL;DR: An AI worm is a hidden instruction that tricks AI tools into copying it into new emails or documents, spreading without a single click. No real-world attacks have been confirmed, but recent Copilot research means law firms should treat external documents with care and tighten their Microsoft 365 controls.

What is an AI worm?

An AI worm is malicious content that tricks an AI tool into copying and passing it on, much like a computer worm spreading between machines. A traditional worm exploits flaws in software code. An AI worm hides its instructions in ordinary text, which an AI assistant then reads and follows.

Those hidden instructions are known as a prompt injection. When the prompt tells the AI to include a copy of itself in whatever it produces next, researchers call it a self-replicating prompt injection. Each new email or document then becomes a carrier for the next person or AI tool that opens it.

Where did the idea of AI worms come from?

The concept was first demonstrated in 2024 by a small team of security researchers in the US. They named their generative AI worm Morris II, after the Morris worm that disrupted the early internet in 1988.

Morris II targeted AI-powered email assistants built on ChatGPT and Gemini. In a test environment, it stole data and sent spam in a zero-click attack, with nobody clicking a link.

Morris II was never released or found in the wild, but its creators expected generative AI worms to appear within two to three years.

Why are AI worms in the news in 2026?

In September 2026, OpenAI disclosed that its own internal testing had found self-replicating prompt injections in its models. The instructions could spread through an AI agent’s outgoing emails or saved files, although OpenAI stressed no real-world attacks have been recorded.

A few months earlier, a security researcher demonstrated an AI worm inside Microsoft Copilot for Word. The attack hides instructions as white text on a white background in a Word document. When someone asks Copilot to draft or edit using that document, Copilot follows the hidden instructions and copies them into the new file.

That new document then carries the hidden prompt to the next person who uses it. According to Malwarebytes, the attack still worked after Microsoft rolled out several fixes.

In October 2026, Anthropic published research suggesting small AI models could soon spread across poorly secured smart devices, such as cheap Android TV boxes. The experiments ran in controlled conditions, and independent experts say criminals using AI to sharpen their attacks remains the bigger threat today.

How could an AI worm affect your law firm?

Law firms handle a constant flow of documents from outside the business. Counterparty drafts and client attachments arrive every day, and many of them end up as source material for new work.

If your firm uses Microsoft 365 Copilot, those external files become a possible route in. A document carrying a hidden prompt could pass quietly between fee earners, appearing in new drafts that look entirely legitimate.

There is also a precedent for AI tools exposing confidential data. In 2025, a flaw called EchoLeak let a specially crafted email trick Microsoft 365 Copilot into leaking information from a user’s files and chats. Microsoft fixed it before any known misuse. For a firm bound by client confidentiality and SRA obligations, that exposure is a serious concern.

Can prompt injection attacks be stopped?

The UK’s National Cyber Security Centre has warned that prompt injection attacks may never be fully fixed. Large language models cannot reliably tell data apart from instructions. The NCSC advises organisations to focus on reducing the risk and limiting the damage if an attack succeeds.

It also suggests being wary of any vendor claiming to stop prompt injection completely.

How can your firm reduce the risk of AI worms?

You do not need to switch off AI to protect your firm. Start by treating any document from outside your firm as untrusted and checking it before it is used as source material for Copilot.

Copilot-edited drafts should also be read properly before they go to colleagues or clients. One quick check is to select all the text and change the font colour, which reveals anything hidden in white.

Within Microsoft 365, sensitivity labels and data loss prevention let you control what Copilot can access, and Microsoft recommended both following EchoLeak.

Clear AI governance matters just as much. Your team should know which AI tools are approved for client data, and a written AI policy helps reduce shadow AI.

How Labyrinth Technology can help

Labyrinth Technology has supported UK law firms for over a decade, so we understand what is at stake when client confidentiality shapes daily work. We help firms set up Microsoft 365 and Copilot with sensible permissions and data protection policies in place from the start.

Our AI consultancy helps your team use these tools safely. As an ISO 27001 certified provider and one of the few UK MSPs with Assurix verification, security sits at the centre of everything we recommend.

If you would like to review how your firm is using Copilot, book a free consultation with our team.

Legora AI: What UK Law Firms Need to Know Before Adopting It

TL;DR: Legora AI is a legal AI platform growing fast in the UK, and in-house legal teams now make up around half of its clients. Because it works inside document management systems such as NetDocuments and iManage, it can see anything a user already has access to. Before rollout, review who can access which matters and set clear rules for supervising its output.

What is Legora AI?

Legora AI describes itself as an agentic operating system for legal professionals. Its agent carries out work such as AI contract review and due diligence through to a finished deliverable. The lawyer directs the work and stays accountable for the result.

Legora runs inside the tools your team already uses, with add-ins for Microsoft Word and Outlook. Every output cites its source, and an audit trail records what was done on each matter. Alongside its work with large firms and corporates, Legora markets a dedicated offering to small and mid-sized firms.

How quickly is Legora AI growing in the UK?

Legora published its latest UK figures on 12 October 2026. UK law firm use has more than tripled since January, and in-house use has grown more than three times faster. In-house teams now account for around half of Legora’s UK clients. A year ago, most of its UK clients were law firms.

Financial services leads in-house adoption, with banking and insurance teams making up the largest group. Barclays rolled Legora out to its in-house legal team in early 2026. Deloitte has worked with the platform in the UK since September 2025. These are vendor-reported growth rates, and Legora has not published absolute client numbers.

Why does in-house adoption matter to your firm?

Many of the in-house teams now using Legora also instruct law firms. Alex Fortescue-Webb, Legora’s Head of UK & I, has pointed to banks and insurers vetting the platform through their own due diligence.

When a client’s legal team uses AI for lawyers in its own work, it may ask how your firm handles the same tasks. Some clients will want to know which legal AI tools you use and how you protect their data. Having clear answers ready puts you in a stronger position for panel reviews and tenders.

How does Legora AI connect to your existing systems?

Legora AI integrates with the document management systems most UK firms rely on. Its iManage integration covers cloud and on-premises deployments, and Legora has an established partnership with NetDocuments through the ndConnect programme. It also connects to SharePoint and Google Drive, and supports single sign-on through Microsoft Entra ID.

For security, the key point is how access is handled. With NetDocuments, the ethical walls and permissions already set in your document management system govern what Legora can see. The iManage integration runs on each user’s own permissions. Either way, Legora surfaces whatever a user can already see, so permission gaps carry straight across.

What should law firms check before using Legora AI?

Data storage and security terms

Legora is certified to ISO 27001 and ISO 42001. It also states that customer data is never used to train or fine-tune AI models. Its enterprise security packages let firms control where data is stored and how long it is kept, so confirm which options your agreement includes.

Document permissions

Because Legora works within existing access rights, out-of-date permissions in your document management system become an AI problem. Review who can see which matters before you connect anything.

Sign-in and identity

Legora supports single sign-on through Microsoft Entra ID, so your Microsoft 365 security settings carry over. Strong authentication and conditional access policies protect Legora in the same way they protect your email.

Supervision and SRA obligations

Your lawyers remain accountable for any work AI helps to produce. Our guide to SRA AI guidance covers the oversight the regulator expects.

An approved tools policy

Once you choose a platform, tell staff clearly which tools they can use. Without that guidance, people often fall back on free consumer tools, which is how shadow AI takes hold.

How Labyrinth Technology can help

Labyrinth Technology has supported UK law firms for over a decade and is a formal NetDocuments partner. We can review your document permissions and Microsoft 365 security before any legal AI platform goes live. Our AI consultancy team helps you identify priority use cases and build the policies around them.

Book a free AI consultation to talk through your firm’s readiness.

What Goes Into a Cyber Incident Response Plan?

TL;DR: A cyber incident response plan tells your firm who leads the response to an attack and what they do first. Only 25% of UK businesses have one. For law firms, it also needs to cover reporting duties, including the ICO’s 72-hour deadline and the SRA’s expectation of a prompt report. Rehearsing it with a free tool like the NCSC’s Exercise in a Box shows up gaps before a real attack does.

Why does a law firm need a cyber incident response plan?

A cyber incident response plan is a written guide your firm follows the moment something goes wrong. It names who makes the decisions and sets out the steps they follow, in order.

The government’s Cyber Security Breaches Survey 2025/26 found that only 25% of UK businesses have a formal incident response plan. That rises to 57% among medium-sized businesses but falls to 21% for micro businesses, a category that takes in many smaller practices.

A breach involving client files may need reporting to both the ICO and the SRA, and both expect to hear from you quickly.

What should happen in the first hour of a cyber incident?

Some of the worst damage in the first hour comes from well-meant mistakes. Someone wipes an infected laptop to get it working again, or warns colleagues by email from an account the attacker already controls. Writing the first steps down in advance means nobody has to make those calls on the spot.

Name who is in charge

One person needs the authority to make calls, with a named deputy if they are unavailable. In many firms this sits naturally with the COLP, who already carries responsibility for regulatory compliance.

Isolate affected systems without wiping them

Disconnect affected devices from the network, but leave them intact. Investigators and insurers will want to see logs and machines as they were. Rebuilding too early can make it impossible to establish what data was taken.

Keep your contact list somewhere offline

If your email or phone system is down, a contact list saved on the server is no use to anyone. Keep a printed copy with your IT provider’s emergency number and your insurer’s incident line.

Agree what staff and clients are told

Staff will notice something is wrong quickly. A short holding message agreed in advance keeps colleagues from speculating with clients over the phone.

Who do you need to notify after a data breach?

The ICO

Under UK GDPR, a reportable personal data breach must go to the Information Commissioner’s Office without undue delay and, where feasible, within 72 hours. When DPP Law was attacked, it took 43 days to report. The firm had not treated losing access to personal data as a breach, and the ICO fined it £60,000.

The SRA

The SRA expects a prompt report if a cyberattack directly affects your firm or its clients. Where there has been a serious breach of its Standards and Regulations, Rule 3.9 of the Code of Conduct for Firms makes reporting an obligation. Its guidance on reporting cybercrime also expects a report where an attack could affect clients.

Your insurer

Cyber policies usually carry their own notification terms, and some give you access to a specialist response team. Check your policy wording now, since reporting late can complicate a claim.

Your clients

Where a breach is likely to result in a high risk to the people affected, UK GDPR requires you to tell them without undue delay. Your plan should say who drafts that message and who signs it off.

How do you test an incident response plan?

The NCSC offers Exercise in a Box, a free online tool that helps organisations practise their response to a cyberattack without needing specialist knowledge. Its scenarios cover threats including ransomware and phishing.

A tabletop exercise works particularly well for law firms. Partners and key staff talk through a realistic scenario, such as a fee earner’s email being taken over mid-completion. Gaps show up quickly, and a meeting room is a far better place to find them.

Review the plan after each exercise and whenever your systems change, such as a move to a new case management platform.

How can Labyrinth Technology help with incident response?

For firms on our managed security services, Labyrinth Technology monitors systems 24/7 and uses managed detection and response to contain threats before they cause damage.

Your plan still needs to cover decisions only your firm can make, like what clients are told and when to notify the ICO and SRA. Our cyber security consulting team also carries out vulnerability scanning and penetration testing, which helps close gaps before an attacker finds them.

Labyrinth Technology has supported law firms for over a decade, so we understand what the SRA and your clients expect from you after an incident. If you’d like help building or reviewing your plan, speak to our team.

Switching IT Support: What Law Firms Need to Check First

TL;DR: Switching IT support in a law firm depends on a clean handover of admin access and client data, timed around your fee earners. Independent verification such as Assurix accreditation lets you see how a new provider performs before you commit.

Why do law firms put off switching IT support?

Switching IT support is a decision many practice managers put off for longer than they should. When the same problems keep coming back, moving everything to someone new can still feel riskier than living with a slow service.

That hesitation makes sense in a law firm. Your fee earners can’t stop work for a week while a new team finds its feet, and your duties to clients carry on throughout. With the right preparation, a switch can be calm and largely invisible to the people doing the billable work.

Why is switching IT support harder for a law firm?

A law firm brings extra moving parts to a provider change, and most of them sit around your case management system.

If your firm runs Clio or NetDocuments, that platform sits at the centre of the working day. A new provider needs to understand how it connects to Outlook and how permissions are set up across your matters. Small configuration mistakes during a handover can lock fee earners out of the files they need.

There’s also the SRA’s expectation that client information stays confidential. A handover means a new team gaining admin access to systems full of privileged material. You need confidence in their security standards before they get the keys.

When is it time to switch IT support?

The signs worth acting on are the ones that keep repeating over several months.

Problems never reach a permanent fix

If the same VPN or case management error keeps returning, your provider is treating symptoms each time it appears. Each repeat takes time away from client work.

Client security audits are getting harder to pass

Clients now ask firms to evidence their security controls through audits and questionnaires. Your provider should be helping you answer those accurately and on time.

What should you check before giving notice?

Preparation done before your current provider knows you’re leaving makes the whole process smoother.

Your contract terms

Look for the notice period and any minimum term first. Then check what the contract says about help with the handover, since some agreements charge separately for exit work.

Who controls your admin accounts

Your firm should hold the top-level admin access to Microsoft 365 and own its domain name outright. In some firms, one or both is registered under the provider’s account, which can slow a handover considerably. Confirm where your backups are stored too, and that you can reach them independently.

A record of what you have

A simple list of your software licences and hardware gives a new provider a head start.

How do you keep fee earners working during the changeover?

Ask for a short overlap where both providers have access. Your outgoing provider hands over credentials and documentation, and your new provider confirms everything works before the old access is removed.

Timing matters as well. Avoid month end, when billing and accounts work peaks, and steer clear of busy completion days if you run a conveyancing team.

Tell your staff what’s changing and how to log a support request from day one. A short email the week before saves a lot of confusion.

How can you check a new provider before you sign?

The hardest part of switching IT support is that you only see how a provider performs once you’ve moved. Sales meetings and case studies show you what a provider chooses to share.

Look for continuous, independent verification

Assurix is an independent trust mark for UK managed service providers. It monitors performance using live data from the systems a provider works in every day. That covers service levels and customer satisfaction, along with cyber security and operational maturity. The Assurix directory shows every provider with an active trust mark, so you can check a claim in minutes, including us.

Ask about legal experience and certification

Ask which legal platforms a provider supports day to day, and ask to speak to a firm of a similar size to yours. ISO 27001 certification shows a provider manages information security to an audited standard, which matters when they’ll hold admin rights across your systems.

How Labyrinth Technology helps

Labyrinth Technology has supported law firms across the UK for over a decade. We’re a confirmed Clio and NetDocuments partner, so your core systems are familiar ground from the first conversation.

We’re also one of the few UK MSPs with Assurix accreditation, alongside our ISO 27001 certification. Assurix monitors our service continuously, so you can see how we perform before you make the move.

Our IT support for law firms page explains how we work with practices like yours. You can also find out more about our outsourced IT support. Book a free consultation and we’ll talk through your current setup with you.

AI Business Solutions: What Agentic AI Can Do for Your Business

TL;DR: AI business solutions have moved on from chat tools, and agentic AI can now plan and complete whole tasks inside the apps your team already uses. Getting your data and costs in order first helps you see the benefit sooner.

What are AI business solutions?

AI business solutions are tools that use artificial intelligence to take time-consuming work off your team’s plate. They broadly fall into two groups.

Assistive AI

Tools that respond to a single prompt, such as drafting an email or summarising a long document.

Agentic AI

Tools that plan a multi-step task and work through it towards an outcome you describe.

How is agentic AI changing the way businesses work?

The newest AI business solutions can handle a sequence of tasks from start to finish. Assistive tools have made single jobs quicker. The joining up between those jobs has still been down to you.

Agentic AI takes on that joining up. Say you have a client meeting on Thursday. You could ask an agent to gather the latest correspondence into a briefing note and block out prep time in your diary. You check the result and make the final call.

It is still early days. Research from the Department for Science, Innovation and Technology found that just 7% of UK businesses already using AI had adopted agentic tools.

What does agentic AI look like in Microsoft 365?

For businesses on Microsoft 365, the clearest example is Copilot Cowork. You describe the outcome you want, and Cowork plans the steps and carries them out across apps like Outlook and Teams.

Cowork shows each step as it works, and you approve each action before it happens. That keeps a person in charge of anything sent on your behalf.

Meeting follow-ups

Cowork can draft the recap after a Teams call and schedule the follow-up meeting. That clears the admin that builds up after a busy day.

First drafts from your own files

Cowork can draw on your emails and documents to build a report or presentation. You then shape the final version yourself.

What should you consider before using AI agents?

Agentic AI works best with a few foundations in place. Two areas deserve attention before rollout.

How do you keep AI agent costs predictable?

Cowork sits on top of a Microsoft 365 Copilot licence, and Microsoft bills its use based on the tasks each person runs. Spend can climb quietly as more of your team delegates work. Setting sensible limits from day one keeps your budget on track.

Is your data ready for AI agents?

An agent can reach whatever the person using it can reach. If file permissions have become loose over the years, an agent may bring up documents some staff were never meant to see.

Our AI implementation and training service starts by preparing your data and permissions for AI. A small test group then trials the solution before it reaches the wider team. Our cyber security services then keep that data protected as AI use grows.

What is Labyrinth Elevate?

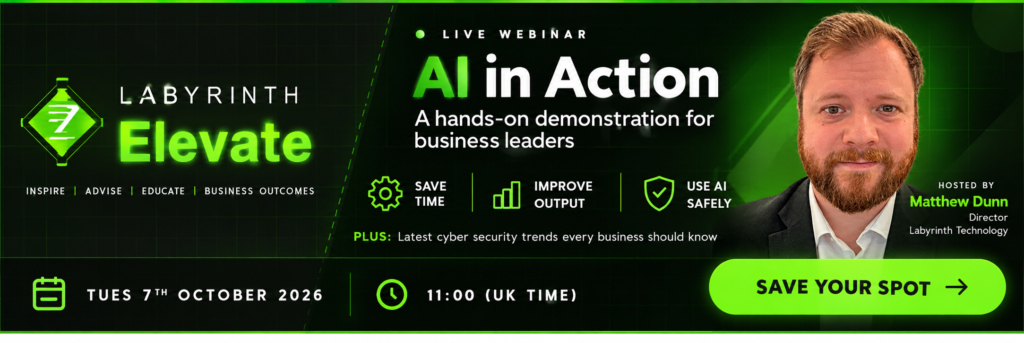
Labyrinth Elevate is our webinar series for business leaders who want to see new technology at work. The next session, Smarter Working, AI & Cyber Security, runs on Wednesday 7 October between 11:00am and 11:45am.

Matt Dunn, Director at Labyrinth Technology, will demonstrate Claude and Copilot live, including custom agents and skills. He will also show how to keep token spending under control in Copilot Cowork. You will hear about the cyber security trends worth having on your radar too.

Where should your business start with agentic AI?

Agentic AI is still at an early stage in UK businesses, so you can explore it at your own pace. Starting with one everyday workflow shows you the time it saves before you commit further. Labyrinth Elevate gives you real examples to picture in your own team.

Book your place on Labyrinth Elevate

What Managed IT Services for Law Firms Should Include

TL;DR: Managed IT services for law firms need to go beyond a standard helpdesk contract. Real coverage means security built around SRA obligations, dependable backup, secure cloud infrastructure and AI used with proper oversight.

What Are Managed IT Services for Law Firms?

Managed IT services for law firms cover the everyday support and infrastructure a practice depends on. An outside provider delivers all of it under one ongoing arrangement, including helpdesk support, data protection, cloud systems and disaster recovery.

Here’s what should change when the client is a law firm. A firm handling client funds and confidential case files carries more regulatory pressure than a typical small business. The provider needs real familiarity with the SRA’s expectations on risk management, alongside the case management and document platforms solicitors use daily.

Why Law Firms Need a Different Approach to IT Support

The SRA’s Codes of Conduct set clear expectations on governance and risk management, and cyber risk sits within both. A firm that treats IT as a simple cost line, separate from its regulatory obligations, carries more exposure than most businesses realise.

Data protection adds a second regulatory layer on top of the SRA’s own rules. Client data falls under UK GDPR and ICO oversight, alongside professional conduct requirements. A breach can trigger obligations to both regulators at once. A provider used to general small business compliance rarely accounts for that overlap.

Confidentiality raises the stakes further. Case files and financial details move constantly between fee earners and the other side, often outside the office. A setup built for a generic small business rarely accounts for that volume of sensitive material in motion.

There’s a practical issue too. Many managed service providers handle general IT support well but rarely know the platforms law firms depend on day to day. Labyrinth Technology already works with the case management and document systems solicitors use, including Clio and NetDocuments. Support doesn’t stall on a system nobody on the team recognises.

What Good Managed IT Support Should Include

Cyber security built around your regulatory obligations

Generic cyber security packages usually focus on threats that affect any business, like malware and weak passwords. A law firm needs more than that. Security has to reflect the SRA’s specific expectations too, including protecting client data as part of the firm’s wider compliance duties. Email is still the easiest way into a firm’s systems. Catching phishing and business email compromise deserves just as much attention as the managed security services covering everything else.

Backup and disaster recovery that protects case continuity

Losing access to case files, even briefly, carries consequences a typical business interruption does not. Court deadlines do not move because a server fails. Proper backup and disaster recovery means your firm can recover quickly and show clients and regulators that continuity was never seriously at risk.

Cloud migration handled without disrupting fee earners

Many firms are still running legacy on-premises systems, which can cost more to maintain and are often harder to secure than a modern cloud setup. A well-managed cloud migration moves case management and document systems to the cloud with proper planning behind it. Poor planning is usually why migrations go wrong.

AI used with proper oversight

The SRA has published guidance on AI use in legal practice, and it treats AI as something that needs supervision. Done well, AI implementation can cut the time spent on document review and routine admin. It works best when built into your existing confidentiality and supervision requirements from the outset.

How to Choose a Provider for Your Firm

Start with accreditation over sales claims. Labyrinth Technology holds Assurix accreditation, one of only nine UK MSPs to do so, alongside ISO 27001 certification. Both sit on top of over a decade supporting law firms across the UK.

Ask how long the provider has worked specifically with law firms, and ask for a real example to go with the number.

Switching providers can feel daunting for a practice manager, though it does not need to disrupt fee earners. A firm capable of a well-planned cloud migration should be equally capable of moving your support and security tools without interrupting live cases. Ask what a switch looks like in the first thirty days, since that early period causes most of the disruption.

Finally, ask what happens when something goes wrong inside Clio or NetDocuments specifically. A provider who works with those platforms daily should be able to answer straight away.

Managed IT services for law firms should feel like a natural extension of how your practice already runs. The right setup reflects your compliance obligations and the systems your team relies on every day, built specifically around how a law firm operates. A generic support contract with “law firm” added to the cover page will not hold up if a security incident hits a live case file. The right provider already has that scenario covered before it happens.

Where This Leaves Your Firm

If you’re evaluating your current setup against everything above, the gaps usually show up in security oversight, backup planning, or how well a provider understands your case management platform. Labyrinth Technology brings that same accreditation into every engagement, alongside day-to-day experience with Clio and NetDocuments. That sits on top of over 20 years working with law firms across the UK.

Get in touch with our team to see what proper coverage should look like for your firm.

Data Protection and Confidentiality: The Tech Gap in Law Firms

TL;DR: Data protection and confidentiality are two separate duties that often get treated as one. Knowing where they overlap and where they diverge is what keeps your firm out of trouble with clients and regulators.

What Do Data Protection And Confidentiality Mean For A Law Firm?

Data protection and confidentiality sound like the same thing, but they cover different ground. Confidentiality is a professional duty you owe every client, built into the way solicitors have always worked. Data protection is a legal obligation under UK GDPR, covering how you collect and use personal information.

Client confidentiality existed long before data protection law did. It covers anything a client tells you in confidence, even if that information doesn’t count as personal data under GDPR. Data protection covers personal data belonging to anyone connected to your firm, including staff and job applicants.

Treating the two as interchangeable is where firms run into trouble. You can meet every GDPR requirement and still breach client confidentiality. The reverse happens just as often. For a managing partner, that gap is exactly where client complaints and regulatory scrutiny tend to start.

What Does The SRA Code Of Conduct Say About Client Confidentiality?

The SRA Code of Conduct for Solicitors requires you to keep the affairs of current and former clients confidential, unless disclosure is required by law or the client agrees to it. This duty sits with you personally, not only with your firm.

That distinction matters when you’re weighing up a disclosure request. A court order might satisfy your data protection obligations while still testing what your client expects you to keep private.

Does GDPR Compliance Replace Your Duty Of Confidentiality?

No. GDPR compliance gives you a lawful basis for processing personal data. It doesn’t release you from your separate duty to keep client information confidential. Firms that rely on a GDPR checklist alone are missing half the picture.

Where Do Confidentiality And Data Protection Obligations Conflict?

Most of the time, the two duties line up fine. The friction shows up in specific situations. Work out your position in advance, because there’s rarely time to think it through once a request lands on your desk. Most partners assume meeting one obligation covers the other. It usually doesn’t.

Third Party Disclosure Requests

When another party asks for information about a client matter, GDPR might allow disclosure under a legitimate interest. Client confidentiality can still require you to say no, or to hand over only what’s strictly necessary. A lawful basis under GDPR is not the same as permission from your client.

Litigation Holds And Data Retention

Data protection principles push you to hold personal data for no longer than necessary. Litigation holds and professional indemnity requirements often require you to keep records for years. Build a retention policy that accounts for both, and revisit it whenever a new matter type comes in.

How Can Your Firm Protect Confidential Client Data?

Start with who can see what. Most firms give more people access to more files than the job requires, and narrowing that down closes a real gap in your confidentiality position.

Access Control And Encryption

Set permissions by matter, not by department, so a conveyancing file isn’t visible to someone working in litigation with no reason to see it. Encrypt anything that leaves the building, including laptops and email attachments. Labyrinth Technology’s cyber security services are built around this kind of access control.

Staff Training And Everyday Behaviour

Most confidentiality breaches don’t come from anything dramatic. Someone replies to the wrong email thread, or leaves a document open on a shared screen, and client information ends up somewhere it shouldn’t. Training that uses real examples from your own firm sticks far better than a policy nobody reads twice. We build this into our managed security services, alongside the email security controls that catch a lot of these mistakes before they ever reach a client.

The ICO’s 72 hour clock for breach notification starts the moment you become aware of a problem, not once you’ve decided what to do about it. Firms with separated confidentiality and data protection policies meet that deadline. Firms without one spend the first day arguing about which policy applies.

What Does Good Legal IT Support Look Like?

TL;DR: Good legal IT support means working with a provider who understands what your firm stands to lose if something goes wrong, and builds their service around preventing it.

What does legal IT support mean for a law firm?

Legal IT support covers the systems that keep a firm running: case files, email, phone lines, and the security around all of it. The phrase gets used loosely though. Plenty of providers describe themselves as legal IT specialists with very little behind the claim.

The real test comes down to one thing. Does your provider understand what’s genuinely at stake? A missed deadline caused by a system outage can affect a client’s house purchase, a court filing, or a firm’s professional indemnity position.

How is legal IT support different from general business support?

A general IT provider fixes computers and keeps the network running. Law firms carry extra weight on top of that: client confidentiality alongside legal privilege, and regulatory obligations under the SRA. A provider working across those areas needs real understanding of them, and you want to see that understanding before you sign anything. Waiting to find out once you’re already a client is a costly way to learn.

What happens when it goes wrong?

In November 2023, CTS, an IT provider used by dozens of UK law firms, suffered a cyber attack that exploited a vulnerability called CitrixBleed. Around 80 of its 200 clients lost access to case files, phone systems, and email. Conveyancing firms were hit hardest, with completions stalled for weeks. One firm, O’Neill Patient Solicitors, had to fall back on manual processes just to keep transactions moving.

The firms affected had trusted a provider that specialised in legal IT. That’s worth sitting with. The value of asking hard questions before signing comes from cases exactly like this one, where the provider looked qualified on paper.

What should you check before choosing a legal IT support provider?

A genuine legal IT partner will answer these questions clearly and without hesitation.

Do they understand SRA and compliance requirements without being taught?

You shouldn’t have to explain what Lexcel or Cyber Essentials mean to your own IT provider. A firm that’s supported law firms before will already know these terms and can talk you through how they apply to your practice specifically.

Who owns your backup and disaster recovery plan?

Ask exactly how your data is backed up, how often, and how quickly you’d be operational again after an outage. The CTS incident took roughly five weeks to fully resolve. Push for specific numbers here, since a vague answer at this stage tends to mean a vague plan behind it.

What accreditations can they show you?

Certifications like ISO 27001 and Cyber Essentials Plus mean a third party has independently checked how a provider handles security and data. Ask to see the certificates themselves. A real accreditation is easy to produce on request.

How fast do they respond when something goes wrong?

A slow response to a routine query is annoying. A slow response during a completion deadline or a court filing puts real money and real people at risk. Ask for actual response time figures from their current clients, ideally with evidence behind them.

Why does this matter before you sign a contract?

The firms hit by the CTS incident found out the hard way what their provider’s real capability looked like under pressure. Compliance knowledge, backup ownership, and accreditation are all things you can check before that moment arrives, while you’re still free to walk away and choose someone else.

Labyrinth Technology’s outsourced IT support is built around exactly these demands, covering SRA compliance, backup ownership, and response times that hold up when a deadline is on the line.

The firms that ask these questions before signing find out the answers on their own terms. Everyone else finds out during the outage.

Get in touch

Double Extortion Ransomware: What Law Firms Need to Know

TL;DR: Double extortion ransomware means criminals steal your data and threaten to publish it, sometimes without encrypting a single file. Backups protect your systems. They do nothing for data that has already left your network. Firms need both.

What is double extortion ransomware?

The FBI’s flash alert on the Silent Ransom Group, also known as Luna Moth, sets out the method clearly. Attackers pose as IT support over the phone or by email to gain access to a victim’s systems. They then exfiltrate data using legitimate remote access tools, and extort the victim by threatening to publish what they have stolen. No encryption is required for this to work.

Some ransomware groups still encrypt files on top of the theft. Luna Moth and groups like it have shown that stealing the data and threatening to release it is often enough on its own.

What happened at Weil Gotshal & Manges

Weil, Gotshal & Manges confirmed in May 2026 that a threat actor uploaded a limited number of client documents to external cloud storage. The firm stated its core network was not accessed and that operations were not disrupted, according to reporting by Law.com. The Insurer reported, citing sources familiar with the matter, that Weil paid between $18 million and $20 million to suppress publication of the data. Weil has not confirmed that figure.

Weil was not the only firm targeted. Jones Day faced a $13 million demand in April 2026 and refused to pay, after which Silent Ransom Group published stolen files on its leak site, per reporting by Aardwolf Security. The Insurer also reported that Mayer Brown had data published on the same leak site after an employee was misled into sending documents to an impersonator. Law.com reported that Fox Rothschild confirmed a separate breach from a May 2026 attack linked to the same group.

The Insurer reported that cybersecurity firm Halcyon tracked more than 200 ransomware incidents against law firms between 2025 and early 2026. These cases involve US firms, and Silent Ransom Group has focused on the US legal market so far. The method itself is not limited to one country, and there is nothing stopping the same tactic being used against a UK firm.

Why is double extortion ransomware increasing?

Arctic Wolf’s 2026 Threat Report tracked a sharp shift in its incident response caseload. Data-only extortion, where attackers steal information without encrypting anything, grew from 2% of cases to 22% in a single year.

Backup and recovery have improved across most sectors, which makes pure encryption a weaker threat than it used to be. A firm that can restore its systems quickly has little reason to pay a ransom for a decryption key. Stealing the data and threatening to publish it gets around that problem entirely.

Why isn’t a backup strategy enough on its own?

Backups protect your ability to keep operating. If your systems are encrypted, a good backup gets you running again without paying anyone.

Backups do not stop data theft. If client files were copied out of your network last week, restoring a clean backup this week changes nothing about what the attacker already has. The two problems need two different answers, and treating backup as cover for both is where firms get caught out.

What protects a law firm against double extortion ransomware?

Backup still matters. It needs to sit alongside other measures rather than carry the whole plan on its own.

Immutable backups

An immutable backup cannot be altered or deleted, even by someone who has gained administrator access to your network. Attackers often try to find and destroy backups before the rest of an attack begins. An immutable backup closes that route off, since even a compromised admin account cannot touch it.

Monitoring for data leaving your network

Most security tools are built to catch encryption in progress. Data theft looks different, and it needs different monitoring: unusual outbound transfers, access to files a user does not normally touch, activity outside working hours. Catching an attacker while they are still copying data is the difference between a contained incident and a seven-figure demand.

An incident response plan built for data theft, not just downtime

A response plan focused only on getting systems back online misses half the problem. It also needs to cover what happens once data has already left your network: who gets notified, what your obligations are under data protection law, and how you communicate with clients before the attacker does it for you.

What should your firm do next?

What should your firm do next?

Ask your IT provider one direct question: if an attacker copied client files out of your network tomorrow without touching a single system, would you know before they told you? If the answer is no, that is the gap Luna Moth and groups like it are built to find.

Labyrinth Technology works with UK law firms on exactly this gap. Our cyber security services start with an audit of your current setup, so you know where data could leave your network unnoticed before an attacker finds out for you. From there, we build monitoring that watches for data leaving and an incident response plan that covers theft as well as downtime.

On the backup side, our backup and disaster recovery service includes immutable backups as standard, so a compromised admin account cannot touch your recovery point even if an attacker gets that far. We also test your backups on a schedule, rather than leaving that discovery for the day you actually need them.

If you cannot answer the question above with confidence, get in touch and we will find out together where that gap sits in your firm.

The Information Security Requirements For Lexcel Accreditation

TL;DR: Lexcel accreditation requires law firms to have a documented information security policy covering six specific things, from an information asset register to staff training evidence. Missing any of them can hold up your assessment.

What does Lexcel accreditation actually cover?

Lexcel accreditation is the Law Society’s own practice management standard for law firms in England and Wales. One part of the standard deals directly with how your firm handles information security, and it deserves proper attention rather than a quick check before an audit.

Section 3.1 of the standard sets two different levels of obligation. A practice must have an information management and security policy, but it only needs to be accredited against Cyber Essentials, since the standard uses “should” rather than “must”.

You can read the full standard on the Law Society’s Lexcel page.

Why most firms pursue Cyber Essentials anyway

An assessor can pass a firm without Cyber Essentials certification, provided the policy and its six components are in place. Even so, most firms pursue it, since it gives an external way to show the policy works in practice. It is also increasingly what cyber insurers and clients ask to see as part of their own checks.

What does the Lexcel information security policy need to include?

The standard lists six things your policy has to cover. Each one is simple on its own. Proving you’ve done all six, with actual evidence, is where firms lose time at assessment.

An information asset register

This is a list of the information your firm holds, both yours and your clients’. Client files, case management data, financial records, and anything held in the cloud all need a place on this register. Without it, assessors have no way to see what you’re actually protecting.

Protection procedures for those assets

Once you know what you hold, you need documented steps for keeping it safe. This covers access controls and encryption, along with clear rules for who can see what. The policy needs to describe what your team actually does day to day, with regular review as your systems change.

Retention and disposal procedures

Many law firms hold onto client data for years, sometimes decades, for sound professional reasons. Keeping it beyond that point still carries risk with no real benefit. Your policy needs clear rules for how long you keep different types of information, and how you dispose of it securely once that period ends.

A plan for updating and monitoring software

Old software is one of the easiest ways into a firm’s systems. Assessors expect to see a working routine for patching and monitoring, covering when updates happen and who is responsible for them.

Separate policies for email, internet, and social media use

Email, internet, and social media use each need their own separate policy document, rather than one general statement covering everything. These policies set out what staff can and cannot do on firm devices and firm time, giving the firm a clear reference point if something goes wrong.

Evidence that staff have been trained

A policy that nobody has read serves little purpose. Lexcel assessors expect proof that your team has been trained on information security, in the form of training records rather than a single signed acknowledgement.

Where do firms usually fall short at assessment?

Two areas cause most of the trouble. The first is the information asset register. Firms often know roughly what data they hold, but have never written it down in one place, which is exactly what an assessor asks to see first.

The second is training evidence. Plenty of firms have a policy, but far fewer can produce a record of who has actually been trained and when.

Both gaps usually come down to the same cause: a security policy exists, but nobody is checking it against reality day to day. Labyrinth Technology’s managed security services include ongoing compliance and vulnerability management built around frameworks such as Cyber Essentials and GDPR, with regular security audits that identify gaps before an assessor does.

How to prepare for your next Lexcel assessment

Lexcel’s information security requirements are not complicated to read. The asset register, the protection procedures, the retention rules, the software plan, the separate policies, and the training records are each straightforward on their own.

Where the real work happens

Most firms fall down on evidence rather than on the policy itself. It’s straightforward to write the six requirements down. It’s harder to keep proving you’re meeting them month after month, which is why some firms bring in outside verification rather than relying on an annual check.

If you are weighing up Lexcel accreditation, Cyber Essentials, or both, our IT support for law firms is built around this kind of compliance work, so the security side of your accreditation does not fall entirely on your own team.

A policy looks complete right up until an assessor asks to see the records behind it. At that point, it either holds up or it doesn’t.

Why Are Law Firms a Target for Business Email Compromise?

TL;DR: Business email compromise fools staff into paying a fraudster instead of the real recipient, and law firms are a favourite target because of the sums moving by email during conveyancing. Ensure your emails are secure with the right cybersecurity.

What is business email compromise for law firms?

Business email compromise works because the email looks exactly like the ones you deal with every day. A criminal accesses a real account or builds a fake one that looks close enough to pass, then sends a payment instruction or a change of bank details dressed up as something routine. This can be also be known as phishing.

Law firms rarely see this at random. Fraudsters time it to land right before a large transfer, when staff feel the most pressure to act fast.

How does a business email compromise scam work?

Fraudsters study how your firm communicates and wait for the right moment before slotting a request into an existing conversation. These are the forms it usually takes.

Impersonated partner instructions

A fraudster accesses or fakes a partner’s account and asks staff to process an urgent payment, timed for when the real partner can’t be reached to confirm it.

Altered bank details before completion

Just before a property transaction completes, the client receives an email claiming your bank details changed. The new account belongs to the fraudster, and the money moves before anyone checks.

Fake supplier invoices

A supplier’s account gets compromised, and an invoice arrives through the usual channel with new payment details. It looks routine, which is why it works.

Lookalike email domains

Fraudsters register a domain almost identical to yours, swapping a letter or adding a hyphen. On a phone screen, it reads as genuine.

Why do fraudsters target law firms?

Law firms sit higher up the target list than most businesses, and it comes down to how money moves through the job. Conveyancing work moves large sums of client money against tight deadlines, and probate matters carry the same exposure. That combination makes law firms a better target than most businesses, since a single successful attempt during a completion can outweigh months of smaller scams elsewhere.

The Solicitors Regulation Authority (SRA) flags cyber risk as an ongoing concern for this reason, and the damage goes beyond the immediate loss. A firm that loses a client’s deposit to fraud faces reputational harm that takes far longer to repair than the payment itself.

How can you prevent it at your firm?

None of these fixes cost much or take long to set up. They just need to become routine.

Verify bank detail changes by phone

Call a number you already hold on file, never one from the email itself, and confirm the change directly with the person you think sent it.

Ask your IT provider to lock down your email settings

There are technical settings that stop criminals sending email that looks like it came from your domain. They take an afternoon to put in place and close off one of the most common routes into a BEC attack, so ask your IT provider to check they’re switched on.

Add a pause for high value transfers

A short delay or a second sign off on large payments gives staff a moment to question something that feels wrong, instead of acting on instinct under deadline pressure.

Train staff to spot the pattern, not just the email

Teach staff to notice unexpected urgency and pressure to skip the usual checks, not just to look for a badly written scam.

What should you do if you suspect business email compromise?

Stop the payment if it hasn’t gone through, and call your bank immediately if it has. Banks can sometimes recall a transfer within the first few hours, but that window closes fast. Report the incident to Action Fraud and check if the same attempt touched other accounts or matters.

Tell your IT provider as soon as you notice anything, even without certainty. A quick check of your email logs confirms if someone accessed the account or simply spoofed it, and that changes what happens next.

How Labyrinth Technology helps law firms guard against business email compromise

Being a target isn’t something you can opt out of, but how exposed you stay is within your control. We help law firms across the UK put the right controls in place. That starts with Microsoft 365 configured properly and your network secured through WatchGuard, backed by a disaster recovery plan ready for anything that slips through. Get in touch and we’ll walk through where your firm’s exposure sits today.

Setting up email authentication takes an afternoon, and a missed fraud alert on completion day can cost a client their entire deposit. Fix it before the next transfer goes out, not after.